Understanding Onion Routing Correlation: Privacy, Threats, and Defenses in the btcmixer_en Era
The digital landscape has long been shaped by the pursuit of privacy, and few technologies embody this quest as profoundly as onion routing. Originally developed to protect government communications, the layered encryption model now underpins a wide spectrum of anonymous browsing tools. At the heart of both the promise and the peril of this system lies a technical phenomenon known as onion routing correlation. This concept refers to the practice of analyzing data patterns, timing, and metadata across the network's layers to de-anonymize users or trace traffic origins. While the architecture of onion routing is designed to obscure the path between client and server, sophisticated adversaries have developed methods to exploit residual information. In niches such as btcmixer_en, where transaction privacy and identity protection are paramount, understanding the mechanics and mitigation strategies of correlation attacks becomes not just technical curiosity but essential operational security.
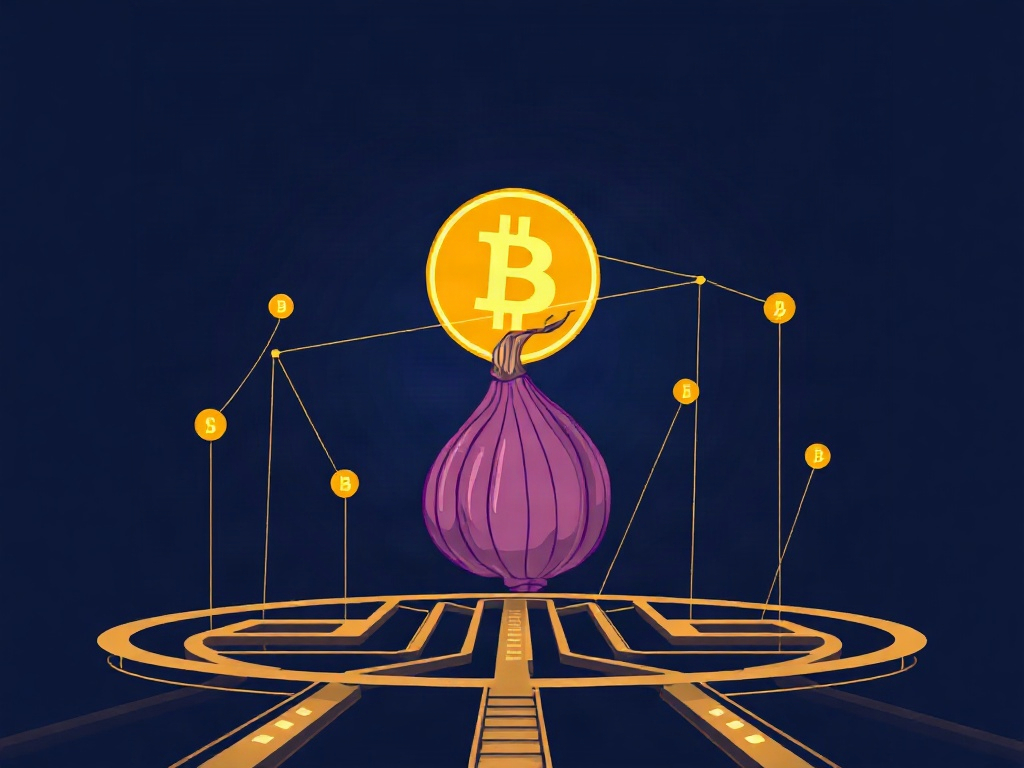
Onion routing operates on a simple yet elegant principle: messages are encrypted in layers, much like an onion, and each intermediate node—typically referred to as a relay—peels away one layer of decryption before passing the packet to the next hop. The final relay, or exit node, decrypts the innermost layer and forwards the plaintext to its destination. No single node possesses the full picture of the communication path, which is the foundation of the network's anonymity guarantee. However, this design introduces subtle vulnerabilities. An adversary who controls or monitors multiple points in the network can perform what is known as a correlation attack, matching traffic patterns entering the network with those exiting it. When combined with timing analysis, packet size observations, and bandwidth profiling, such attacks can significantly reduce the anonymity set.
The Mechanics of Onion Routing and Correlation Risks
How Data Flows Through Tor Nodes
In a typical onion routing circuit, a client selects a random path consisting of three nodes: an entry guard, a middle relay, and an exit relay. Each node only knows its immediate predecessor and successor, preventing any single point from mapping the entire route. The entry guard learns the client's IP address but not the final destination; the middle relay learns only that traffic is passing through but has no knowledge of either endpoint; and the exit relay sees the destination server but not the user's identity. This compartmentalization is the primary defense against casual observation, but it does not inherently prevent a determined adversary with vantage points at multiple network layers from attempting correlation.
Entry, Middle, Exit Node Dynamics
The security of the circuit hinges on the assumption that an adversary does not control or monitor enough nodes to perform end-to-end correlation. Statistical studies suggest that compromising a single entry guard and the corresponding exit relay is sufficient to link a significant portion of traffic, especially when the user's behavior patterns are predictable. Factors such as consistent online schedules, repeated use of the same services, and the unique timing characteristics of certain applications can provide the correlation data needed to bridge the gap between entry and exit. This is where the concept of onion routing correlation transitions from theoretical risk to practical threat vector.
Correlation Attacks: Theory and Practice
Timing Analysis and Traffic Fingerprinting
Timing analysis is perhaps the most widely studied form of correlation attack. The underlying premise is that even though the content of messages is encrypted, the timing patterns—when packets are sent and received—often retain correlation due to the way applications generate traffic. An adversary monitors the volume and timing of packets entering the network at the entry node and compares them with the timing patterns observed at the exit node. If the patterns align within a acceptable margin of error, the probability that the two streams are related increases dramatically. Traffic fingerprinting goes a step further by classifying the type of application or protocol being used based on its distinctive traffic signatures, allowing the adversary to narrow down the user's activity even without knowing the exact content.
Statistical Methods in Correlation
Beyond simple timing matching, sophisticated statistical methods such as cross-correlation coefficients, mutual information calculations, and machine learning classifiers are employed to detect subtle relationships between entry and exit traffic. These methods can handle noise, variable latency, and adaptive traffic shaping techniques. By training on large datasets of labeled traffic, these models learn to recognize the "fingerprint" of a given user's behavior, making it possible to de-anonymize targets who may otherwise appear indistinguishable from the crowd. The arms race between such correlation techniques and privacy-enhancing technologies like traffic padding, chaffing, and adaptive routing underscores the dynamic nature of this field.
Mitigating Correlation Threats in Modern Networks
Multi-hop Path Randomization
One of the most effective defenses against correlation is the randomization of the routing path. Rather than using a fixed three-hop circuit, modern implementations dynamically change the path for each new session or even periodically within a session. By increasing the number of hops and ensuring that no two circuits share the same sequence of nodes, the adversary's ability to correlate traffic is diluted. The probability of controlling or monitoring enough nodes to perform end-to-end correlation drops exponentially with each additional relay, making this approach a cornerstone of robust onion routing design.
Traffic Padding and Noise Injection
Padding involves adding dummy data to messages so that the observed packet size and timing deviate from the application's natural pattern. Noise injection goes a step further by injecting random traffic into the network, creating a cloud of false signals that confound correlation algorithms. When combined with timing obfuscation techniques such as burst sending and inter-packet delay randomization, these methods raise the bar for an attacker, requiring significantly more data and computational resources to achieve a successful correlation. For users operating within the btcmixer_en context, where transaction anonymity is critical, adopting clients and services that support such padding and noise features can provide a meaningful layer of additional protection.
The Role of Mixing Services like btcmixer_en in Privacy Enhancement
How Mixing Integrates with Anonymity Networks
Mixing services, often referred to as tumblers, operate by pooling together transactions from multiple users and redistributing them in a way that breaks the on-chain link between sender and receiver. When such a service is accessed through an onion routing network, the combination of mixing and correlation-resistant routing creates a compounded privacy effect. The mixer obscures the transaction graph, while the onion routing obscures the user's network footprint. In the btcmixer_en niche, users often seek this dual-layer approach to ensure that neither the network layer nor the transaction layer reveals identifying information. The synergy between these technologies exemplifies how privacy is not a binary state but a spectrum of overlapping protections.
Limitations and Best Practices
Despite the theoretical strength of combining mixing services with onion routing, practical limitations exist. A malicious mixer operator could keep logs, perform internal correlation, or collude with network adversaries. Similarly, if a user's device is compromised, or if they fail to properly configure their routing client, the intended anonymity benefits may be undermined. Best practices include using reputable, open-source mixing services, running the latest version of the routing client with all security defaults enabled, avoiding the reuse of circuits for sensitive operations, and employing additional opsec measures such as VPN chaining or disk encryption. Users of btcmixer_en and similar platforms are advised to treat onion routing as one component of a broader privacy stack rather than a standalone solution.
Future Directions and User Responsibility
The evolution of onion routing correlation techniques shows no signs of slowing, and neither does the community's response. Emerging research focuses on information-theoretic anonymity guarantees, quantum-resistant encryption for the routing layer, and decentralized path selection protocols that eliminate trusted nodes altogether. Meanwhile, the integration of privacy-preserving protocols such as Dandelion++, which routes transactions through a randomized gossip network before reaching the broader peer-to-peer layer, represents a convergence of mixing and routing concepts. For the informed user, staying abreast of these developments is not optional but necessary. The landscape of digital privacy is an ever-shifting battlefield, and mastery of concepts like onion routing correlation is essential for anyone serious about maintaining control over their personal data and online identity.
In conclusion, while the technical mechanisms of onion routing provide a strong foundation for anonymity, they are not impervious to correlation attacks. The interplay between routing architecture, traffic analysis, and complementary privacy tools like mixing services defines the actual level of protection achievable. By understanding the risks, implementing robust mitigations, and adhering to operational security best practices, users can navigate the digital realm with a significantly reduced risk of exposure. The btcmixer_en niche, at the intersection of transaction mixing and network anonymity, serves as a pertinent case study in how these technologies can be—or should be—orchestrated for maximum effect.
- Understand the layered path structure and node trust assumptions.
- Employ traffic padding and noise injection to disrupt timing patterns.
- Rotate routing circuits frequently and avoid predictable behavior.
- Combine mixing services with onion routing for compounded privacy.
- Stay updated on emerging correlation countermeasures and protocol upgrades.
- Entry guard selection and longevity for stability against node compromise.
- Circuit randomization schedules
 David ChenDigital Assets Strategist
Analyzing Onion Routing Correlation and Its Implications for Digital Asset Privacy
As David Chen, a digital assets strategist rooted in quantitative analysis and market microstructure, I view the technical architecture of privacy networks through the lens of risk and return. The concept of onion routing correlation sits at the intersection of cryptographic design and observable market behavior, particularly relevant for on-chain analytics and portfolio exposure. In traditional finance, we dissect correlation structures to manage systemic risk; similarly, understanding how layered encryption paths may intersect with metadata leakage is essential for assessing the true resilience of privacy-preserving assets.
From a practical standpoint, onion routing correlation refers to the statistical likelihood that adversaries can de-anonymize traffic by cross-referencing entry and exit node patterns, a concern that directly impacts the usability of privacy coins and layer-two solutions. My quantitative background allows me to model these not as binary failures but as probabilistic risk factors that influence liquidity premiums and hedging strategies. When on-chain data reveals sudden shifts in wallet behavior correlated with known network vulnerabilities, it signals a re-pricing of privacy risk that astute strategists must factor into asset allocation models.
Ultimately, the strategic imperative is to integrate correlation-aware metrics into portfolio oversight without abandoning the privacy ethos that underpins much of the digital asset class. I advocate for a balanced approach: stress-testing exposure against hypothetical correlation scenarios, diversifying across assets with varying privacy postures, and maintaining an active stance on protocol upgrades that mitigate metadata exposure. By treating onion routing correlation as a quantifiable risk variable rather than an abstract technical concern, we can preserve both confidentiality and capital efficiency in evolving market regimes.